Data Security Assessment
AI readiness starts with data readiness, and that starts with a clear understanding of where sensitive data resides, who owns it and how well it is protected. This engagement helps you identify gaps in each of those areas and close the gap to AI readiness.
The purpose of the assessment is to plot your current Data Security Position against our properietary maturity model designed for the age of AI. The journey towards your sensitive data being more secure and governed, begins here with SCC.
Why it matters
Data is your most valuable asset, yet many organisations cannot confidently answer fundamental questions about it: Where does sensitive data reside? Who owns it? How is it protected? And is it ready to support AI adoption?
As businesses accelerate digital transformation and introduce AI-powered technologies, the risks associated with unmanaged, unclassified and poorly governed data increase significantly. The challenge is rarely a lack of technology. More often, the struggle is with fragmented ownership, unclear accountability and limited visibility across the data estate. These gaps can create security, compliance and operational risks that undermine strategic objectives.
The Data Security Position Assessment provides an objective view of your current data security position across Security, Governance, Compliance and Operations. By identifying maturity gaps, risks and opportunities for improvement, SCC helps you prioritise investment, build a realistic roadmap and establish the foundations required for sustainable data protection and reponsible AI adoption.
How it works
Step 1
Kick-off
We walk you through the process and agree who needs to be involved. We also explain the maturity model, the outcomes you can expect and any priority areas you have already identified, so the assessment starts there.
Step 2
Discussion-led assessment
Our consultants run workshops with your team on controls, policies and processes. It is a discussion, not a checklist audit. Your team knows how things work day to day, and that knowledge builds the picture.
Step 3
Technical assessment
Most organisations run more than one data management tool. We assess how mature your data security is across all of them. We can do this with your team or in the background, whichever suits you.
Step 4
Data security assessment report
You get a report and an interactive Power BI dashboard that give you a measurable baseline. Both map what we learned in the workshops and the technical review against the maturity model.
step 5
Deliver your roadmap
We present the findings and a roadmap: what to fix first, what to address within 12 months and where SCC services can help.
Partners

Specialists
Azim Zicar
DATA SECURITY CONSULTANT
Over the last three years Azim has helped organisations assess their maturity, identify risks and develop practical roadmaps that align technology investments with business outcomes.
Learn more about our Data Security Maturity Model
Data security in the age of AI is no longer just a technology challenge. It requires collaboration between different teams to ensure information remains protected and ready for responsible use.
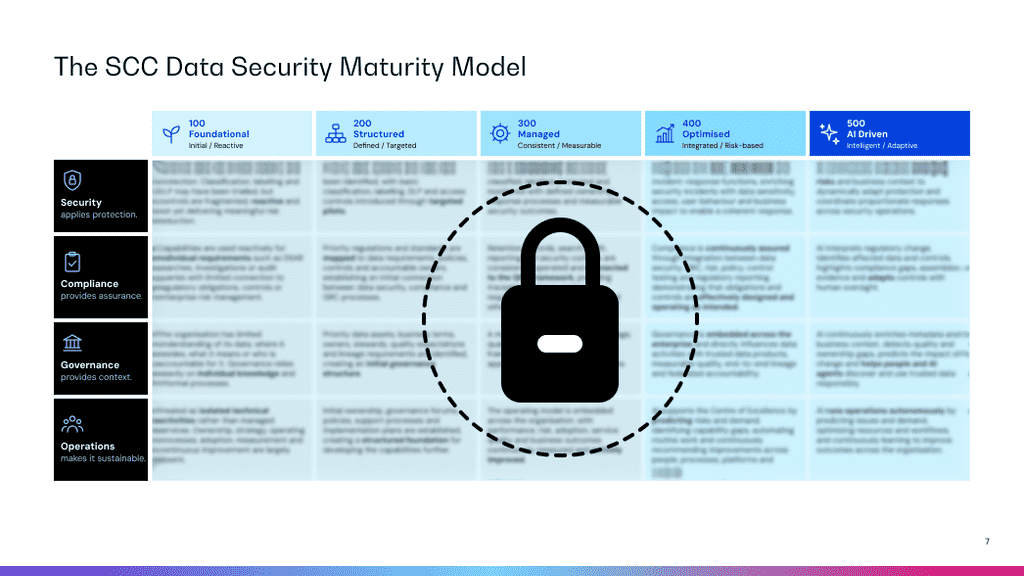
To address this, our specialists developed the SCC Data Security Maturity Model, a practical framework that helps organisations measure their capability across Data Security, Governance, Compliance and Operations, providing a clear view of current maturity, priority risks and opportunities for improvement.
If you’d like to learn more about the thinking behind the model, the maturity levels, and the specific capabilities assessed within each domain, download our article and discover how leading organisations are building the foundations for secure, compliant and AI-ready data.
"*" indicates required fields
FAQs
How long does a data security assessment take?
Typical duration from kickoff to final report is normally 4–8 weeks. SCC will work with your project manager or key stakeholders to agree an aapropriate timeline.
Who do you need to work with from my organisaiton?
As the assessment is looking at both the business and technical operations, a wide range of stakeholders from business and IT will need to be engaged across the different workshops. We typically need 10 hour of their time. Some example roles we regularly engage with are: InfoSec, DPO, Data & AI lead and others.
How much does the assessment cost?
Pricing for the assessment is fixed and may be partially covered by funding offered by some vendors.
What do we actually receive at the end?
A tailored roadmap with an accompanying detailed report and a dashboard that includes a breakdown of your current maturity score. The roadmap addresses the long-term strategic recommendations and is designed to inform investment decisions.
"*" indicates required fields