Financial Services and Insurance.Your regulator wants evidence, not a dashboard.
UK financial institutions are now judged on proving and defending their cyber decisions. SCC opens with decision-grade intelligence through Active Cyber Defence, then runs the regulated estate behind it as one accountable chain, from detection to board-ready evidence.
Cyber stopped being an operations question
The question facing your board is no longer about controls existing. It is proving and defending the cyber decisions you have made, the evidence that informed them and who is accountable. SMCR makes that accountability personal. Senior managers at authorised firms are liable for cyber governance failures by name.
Most security estates were not built to answer that. The tooling produces data. Turning that data into an account a board can use and a regulator will accept still takes manual translation. The gap between detection and defensible evidence is where the exposure now sits.
- £5.74M is the average cost of a UK financial-services data breach, the costliest of any UK sector, against a £3.29M UK all-industry average.
- 58% of large UK FS firms suffered at least one third-party supply-chain attack in 2024.
- 14% continuously assess third-party risk, and that group’s attack rate was 32% against 68% for onboarding-only assessors..
Supervision is live,
not approaching
FCA PS21/3 and PRA SS1/21 reached their transition deadline on 31 March 2025. Remaining within impact tolerances is now a continuous, board-owned obligation.
The Critical Third Parties regime under PS16/24 has been live since 1 January 2025, with major cloud providers among the likely candidates for designation.
The FCA’s new operational-incident and material third-party reporting rules come into force on 18 March 2027, a test most legacy estates cannot yet evidence. The instruments in play: SMCR, SYSC 15A, PRA SS1/21, PS16/24, PS7/26 and the Cyber Security and Resilience Bill. One CISO is accountable across all of them.
How the evidence actually gets produced
Trust in regulated financial services is earned in three layers, each creating the conditions for the next.
Intelligence earns the first conversation:
SCC leads with the regulatory instruments you live under and the operational pressures you would name internally, carrying evidence you can cross-reference against your own experience.
ACD proves operational competence:
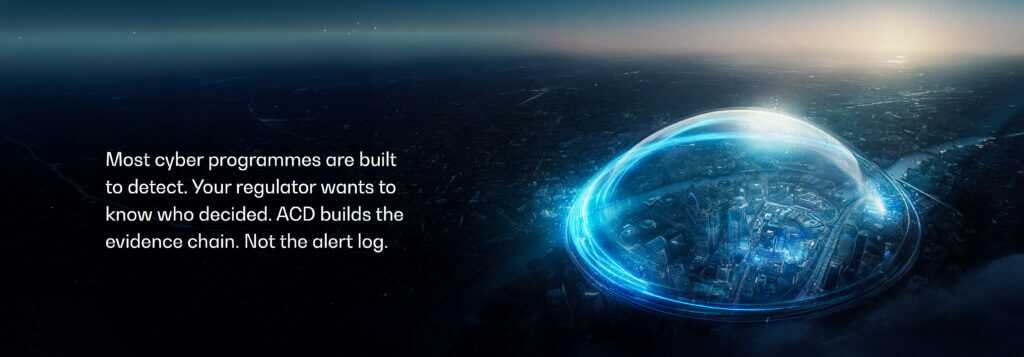
it turns curated threat intelligence, monitoring, automation and expert interpretation into a continuous evidence chain, positioned around defensible decisions rather than alert volumes.
Operating model earns the relationship:
a UK SOC in Birmingham staffed by SCC employees, an in-house configuration centre, vendor relationships 50 years deep and a delivery chain SCC owns rather than subcontracts.
What Active Cyber Defence actually is
Continuous supply-chain risk monitoring
PS16/24 CTP regime and SS2/21 third-party obligations.
Regulatory alignment
SMCR accountability and Cyber Security and Resilience Bill reporting timelines.
Continuous operational monitoring
The detection-to-evidence gap supervisory testing now exposes
Microsoft 365 configuration assurance
FCA operational-resilience evidence requirements and SYSC 15A configuration and change-management obligations. M365 misconfiguration is among the most frequent FSI attack vectors.
One accountable chain, four specialisms
Active Cyber Defence is where most FSI conversations start, but it is one part of how SCC runs the regulated estate. The same operating model one owner, one governed chain, evidence as a standard output runs across operational resilience, digital platforms and the AI you have to defend. Cyber opens the door; the wider chain is what keeps the business running when the next thing happens.
Operational Resilience
Run the regulated estate as one governed delivery chain, so a supplier’s failure is answered in a single voice with evidence on demand. Third-party risk treated as first-party risk.
Digital Platforms
Modernise the estate and exit legacy without disruption, with FinOps proving the commercial value. Sovereign where control matters, hyperscaler where elasticity pays.
Data and AI
Enable and scale the AI you can defend. A data-strategy pathfinder and five defensibility tests keep every model decision explainable, auditable and reversible under Consumer Duty.
What SCC owns, and what that means for you
These are inspectable operating facts, not marketing claims. In a market where most large UK financial firms were hit through a supplier last year, and the CTP regime is bringing cloud providers under direct oversight, who owns the delivery chain carries commercial weight. ACD is proven with NatWest, a UK systemic bank.
“We already have cyber tooling and service partners.”
Tooling is not the issue, and neither is who runs it day to day. Decision quality and evidence quality are where the regulatory pressure now sits, and under SMCR that pressure is personal. You can delegate the work. You cannot delegate the accountability. “SCC is not a known FSI cyber name.” Correct, and the campaign does not pretend otherwise. SCC leads with inspectable capability, regulatory precision and verifiable operating facts.
SCC has operated IT infrastructure for British organisations since 1975. It is the UK’s largest privately owned IT services business, debt-free and family-owned. Its SOC, configuration centre and engineering capability are UK-based and built in-house rather than assembled from partners, which removes the supply-chain risk of partner-delivered work. SCC advises across the vendor market without a fixed product to sell, and places workloads on UK soil or hyperscaler infrastructure according to the requirement.
50 years
Operating critical IT infrastructure for British enterprise since 1975.
Number 1
The UK’s largest privately owned IT services business, family-reinvested.
Sovereign
Owned, operated and jurisdictioned. SOC, configuration centre and engineering on UK soil.
accountable
One accountable operator built ground-up, not partner-assembled.
Book an Active Cyber Defence briefing.
When supervision asks what happened, and who answered for it, could you show them? The review is a working session, not a sales call. An SCC cyber practitioner walks through where your detection-to-evidence gap sits, which regulatory instruments are most exposed and what a continuous evidence chain would change. You leave with a view of your own position.